Key takeout
- The frontend of CoinMarketCap has compromised and has displayed a fraudulent pockets verification popup to the person.
- This violation exploited a backend API vulnerability linked to the platform’s Doodles performance and inspired continued investigation.
Please share this text
The Coinmarketcap frontend was compromised on June twentieth, and its webpage displayed a fraudulent pop-up message and requested guests to verify their crypto pockets. The malicious pop-up was first flagged by a number of crypto group members.
The platform’s groups have checked the incident, investigated the investigation, and warned customers to not join their wallets whereas they have been working to resolve the difficulty.
🚨Safety alerts
We all know that malicious pop-ups have appeared on our web site that encourage customers to “test your pockets.”
Don’t join the pockets.
Our crew is actively researching and dealing to resolve issues.
– coinmarketcap (@coinmarketcap) June 20, 2025
Blockchain safety service supplier Coinspect Safety revealed that CoinmarketCap’s backend API offers manipulated JSON payloads designed to inject malicious JavaScript by way of a rotating “Doodles” function.
coinmarketcap’s backend API manipulates JSON information injecting malicious JavaScript by way of a rotating “doodle” function. The doodles displayed range from go to to go to, so not everybody will see them. The injected pockets drainer is all the time loaded while you entry /doodles / pic.twitter.com/13o9ab7jlw
– Coinspect safety (@coinspect) June 20, 2025
Sure, a CoinMarketCap drainer loaded from a “Doodle” JSON file. Lottie is a JSON-based animation file format that permits designers to simply ship animations to any platform. We’re investigating this injection vector and different web sites and Dapps. https://t.co/hac2pdfe48
– Coinspect safety (@coinspect) June 20, 2025
Additionally at this time, Crypto Briefing seen indicators of the same safety incident on one other standard Crypto web site.
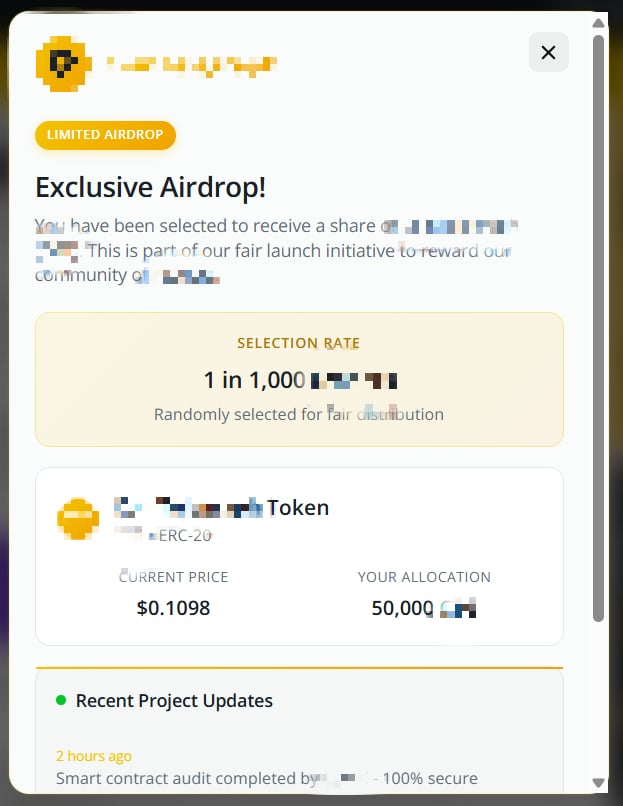
The online web page displayed a pop-up claiming a possibility for “unique airdrops”. This was completely different from the Coinmarketcap incident, however equally inspired guests to insist on airdrops and join their wallets.
Crypto Briefing couldn’t verify whether or not the location’s frontend was compromised, on condition that the suspicious conduct seems to final solely about 5 minutes. The location rapidly returned to regular and the pop-ups have been now not seen.
This violation follows a cybersecurity report from CyberNews 16 billion public passwords It is among the largest information breaches in historical past and impacts entry to main platforms equivalent to Fb, Google, and Apple.
Specialists advocate that customers replace their passwords for all their main accounts, particularly these linked to delicate providers equivalent to work platforms. Customers are extremely really helpful to make use of a password supervisor to generate a robust, distinctive password for every account.
Further safety measures must also be thought of, equivalent to enabling two-factor authentication (2FA) and carefully monitored accounts.
Please share this text