
Share this text
Bitfinex has been within the highlight just lately after a ransomware group named “FSOCIETY” claimed to have accessed 2.5 TB of information on the trade. of Private data of 400,000 customers. In response to the allegations, Bitfinex CTO Paolo Ardoino stated: clarified Database hacking claims It appears like that “Faux” assured person funds are saved secure.
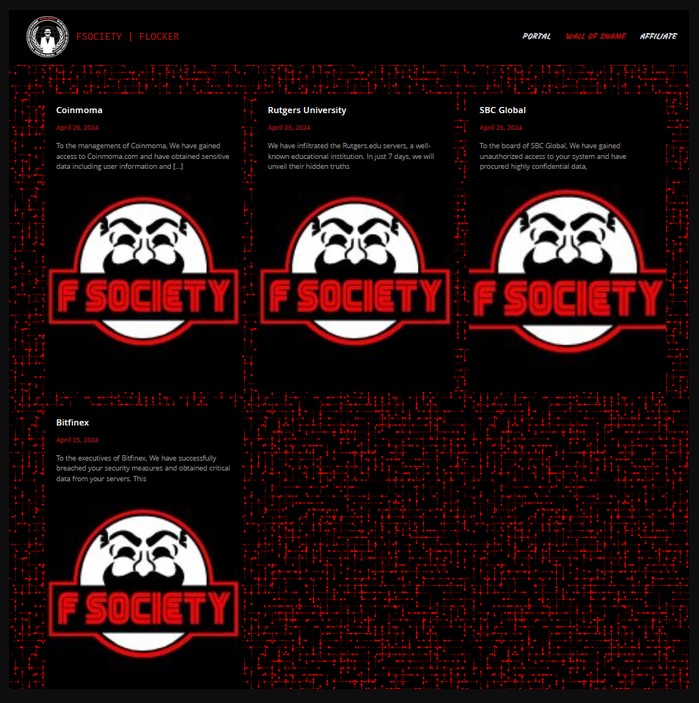
Ardoino discovered It was exterior Discrepancies in knowledge inside hacker posts and inconsistencies in person knowledge.
Hacker posted pattern knowledge containing 22,500 E mail and password data. however, Based on Paolo, Bitfinex doesn’t retailer cleartext passwords or two-factor authentication (2FA) secrets and techniques in cleartext. Moreover, of the 22,500 emails included within the leaked knowledge, solely 5,000 matched Bitfinex customers.
Based on him, this could be a frequent downside in knowledge safety. Customers usually reuse the identical electronic mail and password throughout a number of websites, which can clarify the presence of his Bitfinex-related emails within the dataset.
One other spotlight is the shortage of communication from the hackers. They didn’t report this knowledge breach or contact Bitfinex instantly. negotiate, that’s That is typical conduct for ransomware assaults, which normally contain some type of ransom demand or communication.
Moreover, though details about the alleged hack was posted on April twenty fifth, Bitfinex solely just lately turned conscious of the declare. Paolo stated that if there was a real risk or request, hackers may benefit from Bitfinex’s bug bounty program and buyer assist channels. contact, None of that occurred.
“The alleged hacker didn’t contact us. If they’d actual data, they might have requested Lamson by means of bug bounties, buyer assist tickets, and so forth. nothing discovered request,” wrote Ardoino.
Bitfinex has carried out an intensive evaluation of its programs and has to date discovered no proof of compromise. Paolo stated the group continues to evaluation and analyze all out there knowledge. that Nothing is ignored within the safety evaluation.
After information of the doable breach surfaced, Shinoji Analysis X person, It was confirmed The authenticity of the leak. The person tried one of many passwords included within the leaked data. be 2FA.
Nevertheless, at press time, he had deleted the publish and corrected his earlier data.
I deleted the unique BFX hack publish because it can’t be edited. What seems to have occurred is that this “Flocker” group has curated an inventory of BitFinex logins from different breaches.
They then made this website appear like a ransom demand for an enormous breach.
— Alice (e/nya)🐈⬛ (@Alice_comfy) May 4, 2024
In one other publish about X, Ardoino advised that the actual motive behind the exaggerated infringement claims is to promote hacking instruments to different potential scammers.
The purpose is to generate buzz round these high-profile (Bitfinex, SBC International, Rutgers, Coinmoma) hacks and promote their instruments, thereby encouraging others to carry out related assaults. They declare they’ve the potential to make some huge cash.
This can be a message from safety researchers (as an alternative of panicking, dig a bit of deeper).
“I feel you are beginning to perceive what is going on on and why they’re sending you messages claiming you have been hacked.
The message within the ticket screenshot is from somebody. pic.twitter.com/YjwG2eeXw2— Paolo Ardoino 🍐 (@paoloardoino) May 4, 2024
Moreover, they questioned why they would wish to promote hacking instruments for $299 if the hackers really accessed Bitfinex and obtained useful knowledge.
Share this text